Showing posts with label Hack. Show all posts

Monday, August 29, 2016

REQUEST A QUOTESEE A DEMO SQL Injection Cheat Sheet & Tutorial: Vulnerabilities & How to Prevent SQL Injection Attacks

What is SQL Injection?
SQL injection is a type of web application security vulnerability in which an attacker is able to submit a database SQL command that is executed by a web application, exposing the back-end database. A SQL injection attack can occur when a web application utilizes user-supplied data without proper validation or encoding as part of a command or query. The specially crafted user data tricks the application into executing unintended commands or changing data. SQL injection allows an attacker to create, read, update, alter or delete data stored in the back-end database. In its most common form, a SQL injection attack gives access to sensitive information such as social security numbers, credit card numbers or other financial data. According to Veracode’s State of Software Security Report, SQL injection is one of the most prevalent types of web application security vulnerability.

Key Concepts of a SQL Injection Attack

  • SQL injection is a software vulnerability that occurs when data entered by users is sent to the SQL interpreter as a part of a SQL query.
  • Attackers provide specially crafted input data to the SQL interpreter and trick the interpreter to execute unintended commands.
  • Attackers utilize this vulnerability by providing specially crafted input data to the SQL interpreter in such a manner that the interpreter is not able to distinguish between the intended commands and the attacker’s specially crafted data. The interpreter is tricked into executing unintended commands.
  • A SQL injection attack exploits security vulnerabilities at the database layer. By exploiting the SQL injection flaw, attackers can create, read, modify or delete sensitive data.

SQL Injections: The Most Prevalent Type of Application Security Vulnerability

With more than 20 percent of all web vulnerabilities being attributed to SQL injection, this is the second most common software vulnerability. Therefore, having the ability to find and prevent SQL injection should be top of mind for web developers and security personnel. In general, a SQL injection attack exploits a web application that does not properly validate or encode user-supplied input and then uses that input as part of a query or command against a back-end database. For example, a typical form may ask for an ID and create a URL: "http://www.somewebsite.com/id/id.asp?id=somedata". An attacker using SQL injection may enter "somedata or 1=1". If the web application does not properly validate or encode the user-supplied data and sends it directly to the database, the reply to the query will expose all IDs in the database, since the condition "1=1" is always true. This is a basic example, but it illustrates the importance of sanitizing user-supplied data before using it in a query or command.

SQL Injection Video

The following video tutorial on SQL injection walks you through more on topics such as "what is SQL injection?" "methods of SQL injection protection" and "how to avoid a SQL injection attack."

SQL Injection Example

Let’s look at the example code below.
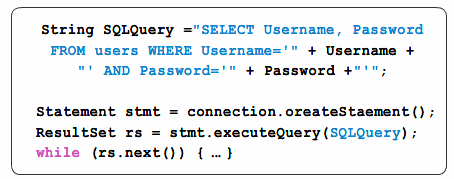
sql injection code
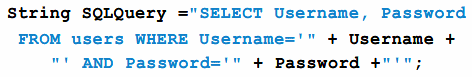
You will notice that user input is required to run this query. The interpreter will execute the command based on the inputs received for the username and password fields. sql injection query
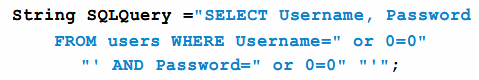
If an attacker provides ‘or 0=0’ as the username and password, then the query will be constructed as:
String SQLQuery =”SELECT Username, Password FROM users WHERE Username=” or 0=0” AND Password=” or 0=0”;
sql injection tutorial
Since under all circumstances, zero will be equal to zero, the query will return all records in the database. In this way, an unauthorized user will be able to view sensitive information. 
Preventing SQL Injection

  • You can prevent SQL injection if you adopt an input validation technique in which user input is authenticated against a set of defined rules for length, type and syntax and also against business rules.
  • You should ensure that users with the permission to access the database have the least privileges. Additionally, do not use system administrator accounts like “sa” for web applications. Also, you should always make sure that a database user is created only for a specific application and this user is not able to access other applications. Another method for preventing SQL injection attacks is to remove all stored procedures that are not in use.
  • Use strongly typed parameterized query APIs with placeholder substitution markers, even when calling stored procedures.
  • Show care when using stored procedures since they are generally safe from injection. However, be careful as they can be injectable (such as via the use of exec() or concatenating arguments within the stored procedure).

SQL Injection Cheat Sheet

The following SQL Injection Cheat Sheet provides a summary of everything you need to know about SQL injection. The SQL Injection Cheat Sheet contains the key concepts of a SQL injection attack, a SQL injection example and tips to avoid a SQL injection hack.

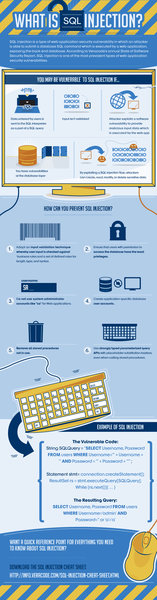
"What is SQL Injection?" an Injection Attack Infographic

To further illustrate injection attacks and preventative steps, we've created this original infographic titled "What is SQL injection," which serves as a visual tutorial to demonstrate how you might be vulnerable to injection attacks, how you can prevent SQL injection and an additional example of SQL injection. If you like this infographic, please share it. And you can embed it on your website with the HTML code below it.
sql injection infographic

Add This SQL Injection Infographic to Your Website

Share:

Sunday, August 28, 2016

3 Basic Tips To Prevent A DDoS Attack

 DDoS Attack

Distributed denial-of-service (DDoS) attacks are always in top headlines worldwide, as they are plaguing websites in banks, and virtually of almost every organization having a prominent online presence. The main cause behind the proliferation of DDoS attacks is that there is a very low-cost that the attacker has to incur to put such attack in motion. Fortunately, today various prevention methods have been developed to tackle such attacks. Before delving further into understanding about the ways to prevent DDoS attack, let’s first understand what exactly a DDoS attack is!

Understanding DDOS Attack

 DDoS Attack bot
A DDoS (distributed denial-of-service) attack is an attempt made by attackers to make computers’ resources inaccessible to its anticipated user. In order to carry out a DDOS attack the attackers never uses their own system; rather they create a network of zombie computers often called as a “Botnet” – that is a hive of computers, to incapacitate a website or a web server.

Let’s understand the basic idea! Now, the attacker notifies all the computers present on the botnet to keep in touch with a particular site or a web server, time and again. This increases traffic on the network that causes in slowing down the speed of a site for the intended users. Unfortunately, at times the traffic can be really high that could even lead to shutting a site completely.

3 Basic Tips to Prevent a DDoS Attack

There are several ways to prevent the DDOS attack; however, here in this guest post I’ll be covering three basic tips that will help you to protect your website from the DDoS attack.

1. Buy More Bandwidth.

 DDoS Attack bandwidth
One of the easiest methods is to ensure that you have sufficient bandwidth on your web. You’ll be able to tackle lots of low-scale DDOS attacks simply by buying more bandwidth so as to service the requests. How does it help? Well, distributed denial of service is a nothing more than a game of capacity. Let’s suppose you have 10,000 computer systems each distributing 1 Mbps directed towards your way. This means you’re getting 10 GB of data that is hitting your web server every second. Now, that’s causes a lot of traffic!

So to avoid such issue, you need to apply the same rule intended for normal redundancy. According to this technique, if you wish to have more web servers just multiply around diverse datacenters and next make use of load balancing. By spreading your traffic to various servers will help you balance the load and will most likely create large space adequate to handle the incessant increase in traffic.
However, there’s a problem with this method that is buying more bandwidth can be a costly affair. And as you’ll know that the current DDoS attacks are getting large, and can be a lot bigger exceeding your budget limit.

2. Opt for DDoS Mitigation Services.

A lot of network or Internet-service providers render DDoS mitigation capabilities. Look for an internet service provider having the largest DDoS protection and mitigation network, automated tools, and a pool of talented anti-DDoS technicians with the wherewithal to take action in real-time as per the varying DDoS attack characteristics. A viable alternative is to utilize a DDoS prevention appliance, which is specifically intended to discover and prevent distributed denial-of-service attacks.

3. Restricted Connectivity.

 DDoS Attack
In case you have computer systems that are connected to the web directly, a better idea is to properly install/configure your routers and firewall so as to limit the connectivity. For an instance, while receiving some data from a client machine you can only allow traffic to pass from the machine only on a few chosen ports (like HTTP, POP, SMTP etc.) via the firewall.

Wrapping Up!


Websites are largely getting attacked by hackers every second. Denial-of-service attack is insanely getting huge and is creating a lot of problems for business organizations having strong online vicinity. In this guest post you’ll not only understand what a DDoS attack actually means, but will also come to know about a few type of methods to prevent DDoS attacks. Aforementioned are three tips that I’ll recommend you to run through to at least understand where to get started towards building a resilient web network with chances of surviving a DDoS attack.
Share:

12 Simple Steps To Become A Hacker

Steps to become a hacker
Hacking is an engaging field but it is surely not easy. To become a hacker one has to have an attitude and curiosity of learning and adapting new skills. You must have a deep knowledge of computer systems, programming languages, operating systems and the journey of learning goes on and on. Some people think that a hacker is always a criminal and do illegal activities but they are wrong. Actually many big companies hire hackers to protect their systems and information and are highly paid. We have prepared a list of 12 most important steps necessary to become a hacker, have a deeper look

1. Learn UNIX/LINUX

linux operating system
UNIX/LINUX is an open source operating system which provides better security to computer systems. It was first developed by AT&T in Bell labs and contributed a lot in the world of security. You should install LINUX freely available open source versions on your desktops as without learning UNIX/LINUX, it is not possible to become a hacker.


2. Code in C language 

c programming
C programming is the base of learning UNIX/LINUX as this operating system is coded in C programming which makes it the most powerful language as compared to other programming languages. C language was developed by Dennis Ritchie in late 1970’s. To become a hacker you should master C language.

3. Learn to code in more than one Programming Language

programming languages

It is important for a person in the hacking field to learn more than one programming. There are many programming languages to learn such as Python, JAVA, C++. Free eBooks, tutorials are easily available online.

4. Learn Networking Concepts

computer networking
Another important and essential step to become a hacker is to be good at networking concepts and understanding how the networks are created. You need to know the differences between different types of networks and must have a clear understanding of TCP/IP and UDP to exploit vulnerabilities (loop holes) in system.
Understanding what LAN, WAN, VPN, Firewall is also important.
You must have a clear understanding and use of network tools such as Wireshark, NMAP for packet analyzing, network scanning etc.

5. Learn More Than One Operating Systems 

operating system
It is essential for a hacker to learn more than one operating system. There are many other Operating systems apart from Windows, UNIX/LINUX etc. Every system has a loop hole, hacker needs it to exploit it.

6. Learn Cryptography

cryptography encryption
To become a successful hacker you need to master the art of cryptography. Encryption and Decryption are important skills in hacking. Encryption is widely done in several aspects of information system security in authentication, confidentiality and integrity of data. Information on a network is in encrypted form such as passwords. While hacking a system, these encrypted codes needs to be broken, which is called decryption.

7. Learn more and more about hacking

hacking or hackers
Go through various tutorials, eBooks written by experts in the field of hacking. In the field of hacking, learning is never ending because security changes every day with new updates in systems.

8. Experiment A Lot

experiment
After learning some concepts, sit and practice them. Setup your own lab for experimental purpose. You need a good computer system to start with as some tools may require powerful processor, RAM etc. Keep on Testing and learning until you breach a system.

9. Write Vulnerability (Loop hole program)

hacking vulnerability

Vulnerability is the weakness, loop hole or open door through which you enter the system. Look for vulnerabilities by scanning the system, network etc. Try to write your own and exploit the system.


10. Contribute To Open Source Security Projects

open source software
An open source computer security project helps you a lot in polishing and testing your hacking skills. It’s not a piece of cake to get it done. Some organizations such as MOZILLA, APACHE offer open source projects. Contribute and be a part of them even if your contribution is small, it will add a big value to your field.

11. Continue never ending Learning 

learning hacking
Learning is the key to success in the world of hacking. Continuous learning and practicing will make you the best hacker. Keep yourself updated about security changes and learn about new ways to exploit systems

12. Join Discussions and meet hackers 

discussion
Most important for a hacker is to make a community or join forums, discussions with other hackers worldwide, so that they can exchange and share their knowledge and work as a team. Join Facebook groups related to hacking where you can get more from experts.
Share:

Watch 18+ Videos On Youtube Without Signing In 2016

Watch 18+ Videos On Youtube Without Signing In
Sometime its annoying when youtube ask you to sign in for your age verification to watch 18+ videos. So i will make it easy for you by showing you a simple youtube trick to watch adult or 18+ youtube videos without signing In. This trick is 100% working as of 2013. So lets get started.

How To Watch 18+ Youtube Videos Without Logging In ?

1. First get the Url of video you want to watch. As shown below.
http://www.youtube.com/watch?v=4Xkh6j7RMqk 
2. Then copy the Video Id. For above link video Id is 4Xkh6j7RMqk
3. Now paste the Video Id in the link given below.
http://www.youtube.com/v/VideoId?fs=1
  • Replace VideoId with the Id you copied in Step 2
4. Now the url will become as shown below.
http://www.youtube.com/v/4Xkh6j7RMqk?fs=1
5. Done.
Share:

Tracking A Person : By Facebook / By Cell Number / By Email.


Internet is filled with people who love to annoy and give out threats. If they are careless, they can be easily tracked, but if it is a professional guy, he might be difficult to trace as he might be using proxy/anonymity tool.
If you think you are in trouble, i would advise you to go to cops. But if you think it is some punk ass guy, follow this tutorial to track him down and kick his ass.
To track him down, you can use mobile number, an email from him, or his Facebook ID.
So lets get it started :


Tracking Somebody By His Facebook ID :


Facebook is full of stalkers and annoying people and fake profiles,  And there is absolutely no way to get rid of them. Sure you can ignore them, but they will start posting on your walls, block them, they will make a new ID. Only way to get rid of them is to muscle them out. And by muscle i mean hack and destroy their PC. To do that, you will need their IP Address, And This tutorial will teach you how to do it.Also we will tell you how to track that person down to his house !
So buckle up.


So we will divide this tutorial in two main parts :

-Getting His IP Address.
-Tracking His IP Address to find his physical location.

Step One : Finding His IP Address :


To do this, we will use the " netstat " command in windows (xp,vista,7,8, doesn't matter), this command will list the active connections and listening ports,and to this this, first you have to invite that person to chat, chat with him for 1-2 minutes, then open your command prompt ( start-cmd ) and then type the following command on it :

netstat -an


And you will get all established connections IP addresses. Note down the suspicious IP’s.

TIP : If you get a whole lot bunch of IP's , close the additional tabs in your browser and terminate the application like antivirus/download managers and retry.


Step Two : Tracing His IP Address :


Once you have got the IP Address you want, its time to trace it. To do that we will need awebsite that give us tracing/ tracking options, some of the best sites are :

http://www.ip-adress.com/ip_tracer/

All these sites can trace the IP Address to his location, and they are pretty easy to use , just jot the IP you noted and put it in their search engine.

Tracking Him Down By His Cell Number :


Are you getting prank calls, or vulgar threats, or simply annoying calls from somebody who doesn't give out his name.
It is pretty easy to track somebody by his cell/landline number. All you got to do is note down his/her number and enter it in this website and it will give you out the details :
http://www.truecaller.com/


Tracking Him Down by His Email Address :


Tracking Email is not new, it has been around since the emails were invented. But the tracking service has definitely got better since them. Email Tracking is comparatively easy than Facebook tracking, all you got to do is follow these simple steps and BAM ! you know the location of the 
sender/reader !


You can use the free service provided by these sites, all you got to do is attach this tiny littleattachment and they will tell you when the reader location is determined. Good thing is that even proxy can't hide the reader. So try them out :
Share:

Remove ads from Kindle special offers

Facing the same problem as other facing?. Want to get rid of annoying ads?. Well for that there are two solutions. Either you pay the amount i.e $30 ( it actually depends on how many ads you have seen) and get rid of it officially or do some engineering and get rid of it. Let me explain first why are you seeing these ads. The price of kindle with special offer is surprisingly low as compared to without it. Actually, if you bought a kindle with special offers so you signed an agreement that you will see these ads as compensation of discount they provided in other words you are seeing these ads for the discount you get on it. Remove ads from kindle.

Remove ads from kindle [Method A]

Now you know why you are seeing these ads. Fist I’ll guide you how to do it legally so called officially as guided by amazon officials just follow the steps below and get rid of it. You can unsubscribe from amazon ads and sponsor screensavers. You will be charged once to unsubscribe it cost varies as explained above. This amount can’t be paid via Amazon Gift card amounts on your account. This can only be paid via one-click payment method.
  1. Navigate to Manage your content and devices
  2. Choose your device tab
  3. Tap on device to get more information
  4. Tap on edit, next to Special Offers then follow the steps in order to unsubscribe it.
  5. The amount will be shown before you proceed to one click method payment.
  6. Confirm it and you are done. Remove ads from kindle.
After the payment is made you will get an email regarding it as notification.

Remove ads from kindle [Method B]

Moving on the second method, it doesn’t cost you a penny. This method is in grey hat area it is not fully legal or illegal . Follow the steps and you will get rid of it.
Disclaimer: I am not responsible for anything or happen to you or your device using this method. Use it on your own ease.
  1. Ensure that your PC is settings are to “Show hidden files and folders” and that it isn’t set to “Hide protected operating system files“.
  2. Connect your kindle device to your computer via USB cable..asset folder Remove ads from kindle.
  3. Open your kindle via windows explorer. Go to the system folder there you find a folder named as “.assets”
  4. Delete the folder “.assets”
  5. Now all you have to do is to create an empty file named as “.assets” in the same destination where it was before i.e in the system folder. The simplest way for doing this is, create a text document file on the desktop as “.assets”. Then copy it and paste it in the system folder. It may ask for confirmation confirm it and now you are done. These empty file resists amazon to create its file again.
  6. Now as .assets folder is no more and we make a fake file there. So amazon server could not make folders and establish connections. It assumes that you are offline and not connected to the internet. The following message will appear on the screen.
    After a couple of mins, it turns to the stock wallpaper which in my opinion is much more decent and less annoying.
    Hope it works for you.  If you know a better trick to Remove ads from kindle let me know. I’ll include it in the update. Remove ads from kindle.
Share:

as